
02.01
CISO / CISO-as-a-Service
Strategy, roadmap, board reporting, security ownership.
Cyber & Information Security Lead · CISO-as-a-Service · ISMS & GRC
I build and run ISMS programmes from the first gap analysis to the certification audit, on the office floor and the plant floor alike. And I go beyond paper: I make sure the SOC sees the threats, the vulnerabilities get fixed and the plant keeps running when an incident hits.
A.01 — Profile
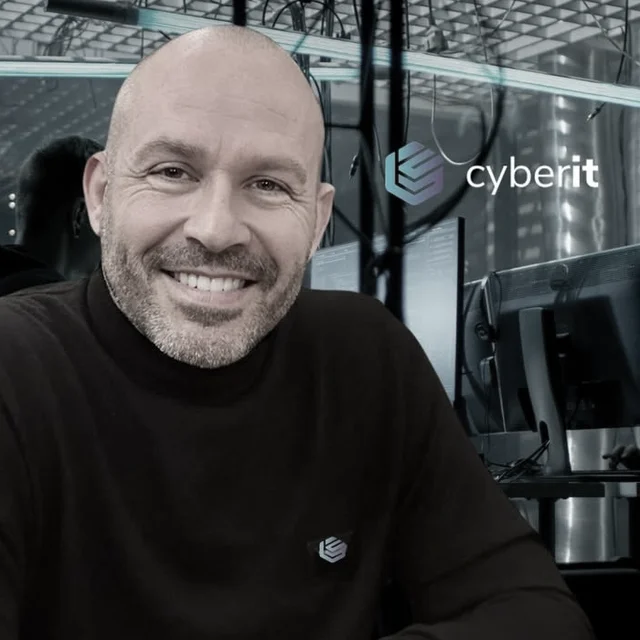
Freelance cyber and information security lead. Before moving into security, I spent ten years in infrastructure, network, and data centre engineering. That is why I can talk to a board about risk in the morning and sit with a firewall or SOC team in the afternoon.
A.02 — Services
02.01
Strategy, roadmap, board reporting, security ownership.
02.02
Scope, risk method, SoA, policies, controls, evidence, internal audit, certification.
02.03
ISO 27001/27002, NIS2, CyFun, DORA, GDPR, CIS Controls, NIST CSF.
02.04
Risk analyses, CIA classification, TARA, third-party and vendor risk.
02.05
Drata, Vanta, ServiceNow GRC, CyberManager (IRM360).
02.06
IT/OT segregation, OT asset visibility, plant security roadmaps.
02.07
SIEM and SOC set-up, detection use cases, incident handling and follow-up.
02.08
ISO 27001 internal audits, gap assessments and control testing.
02.09
Scanning at scale, risk-based prioritisation, closure tracking with IT and plant operations.
02.10
Network and OT segmentation, firewall and proxy review, secure-by-design input for new sites.
02.11
Privileged access management, access reviews, least-privilege rollouts.
02.12
Azure and AWS hardening, cloud posture monitoring, code and dependency scanning.
02.13
Security awareness campaigns, phishing simulations, NIS2 and CyFun training.
02.14
Scoping and test planning, findings review, remediation tracking to closure.
A.03 — Clients
A.04 — Technology partners and platforms


A.05 — Experience
Stellantis
Cyber Security Expert & Project Manager IT/OT/IIoT
IT/OT/IIoT security roadmap for the Sint-Truiden, Metz and Mirafiori plants: Octoplant, TXOne, Qualys, SOC integration, BeyondTrust remote access and Defender for Endpoint. 4,000+ assets covered, 1,500+ vulnerabilities closed, no plant downtime. Roadmap to ISO 27001 and NIS2.
AARIXA
NIS2 & ISO 27001 Implementer, Project Manager
NIS2 and ISO 27001 implementation with CyberManager (IRM360) as ISMS and GRC platform: gap analysis, asset inventory, risk register, policies, evidence library, internal audits, and Stage 1 and Stage 2 audits with Bureau Veritas.
Flemish Government (VCDV)
Information Security Officer & Risk Analyst
ISO 27001 implementation and internal audits, NIS2 and CyFun trajectories for several entities. ISMS risk dashboard with classification, CIA ratings and DPIAs. Risk analyses on business applications with remediation follow-up. NIS2/CyFun workshops for 1,400+ local governments.
INEOS
NIS2 & ISO 27001 Consultant, Project One
Advisory on NIS2 and ISO 27001 for Project One, the new INEOS site in the Port of Antwerp.
BNP Paribas Fortis
Third-Party Technology Risk Officer
Assessed suppliers and critical ICT services against DORA third-party risk requirements, within the bank's technology risk processes.
Coreso
Information Security Officer & ISO 27001 Implementer
Built the ISMS in Drata from scratch: policy set, risk register, controls and evidence library, aligned with ISO 27001, NIS2 and CyFun.
TotalEnergies
CISO Benelux
Security owner for 300+ applications and 2,500+ users; ISO 27001 and NIS2 with an ISMS in CyberManager. Security lead for network segregation, IAM/MFA, CyberArk, Zscaler, Sentinel and Defender. Vulnerability and incident handling with the group SOC, pentests, firewall change reviews.
Arrow Electronics
Information Security Officer & SOC Engineer
Led MSP customers through ISO 27001 and NIS2. Vulnerability management and detection with Tenable, Splunk, CrowdStrike and Defender. Backup and storage designed as a ransomware recovery layer: immutability and restore tests.
PCS Innotec International
System & IT Security Engineer (BE, FR, NL, UK)
Hardened Azure and Microsoft 365: Defender, Entra ID, CyberArk PAM, Intune, Sentinel. Firewall and remote access security across four countries with Check Point and FortiGate. Implemented an ISMS.
Luminus
Network Engineer, IT Security workstream
Network access control and perimeter security for the migration of two data centres: Cisco ISE, Zscaler, Check Point, F5. IAM and PAM with CyberArk; IT/OT segmentation for the new head office.
Medtronic
Medior Security Officer, Global Operations Center
Secured the global data centre estate of a medical device manufacturer: Check Point, Palo Alto, Fortinet, CyberArk, AWS. Change and incident management under regulated audit requirements; GRC set-up in Vanta with policies and risk analyses.
Euroports
Cloud Security Engineer
Azure AD clean-up, patching and hardening, monitoring in Azure and AWS, Defender for Endpoint, Entra ID and Intune.
Cegeka / Crelan
System Engineer, backup and data centre migration
Owned the bank's backup platform during the outsourcing to Cegeka. Migrated the data centre from Anderlecht to Hasselt and Heerlen after a full CMDB audit, then tested HA, failover, RPO and RTO.
Cochlear
Network Security Services Engineer, EMEA / AU / US
Firewall and network security for international sites: Check Point, Fortinet, Cisco, VLAN redesign.
ENI gas & power
Infrastructure Engineer
Set up IAM, MFA, SSO and IT asset management. BitLocker disk encryption, AD auditing, FortiGate and BlueCoat, physical access control (iProtect).
TotalEnergies Benelux
Technical IT Team Lead (Belgium – Netherlands)
Led a team of 8 engineers on the Benelux workstation roll-out, including the Vlissingen refinery, The Hague and Brussels: SCCM, software deployment, ITSM and incident management.
Pfizer (via HP)
System Administrator & IT Coordinator
Team lead for hard drive encryption and disaster recovery planning. ITIL change, incident and configuration management in a GxP environment; reviewed SOPs during the move to HP.
SCK CEN and VITO, Truvo, Syntigo (NMBS)
System Administrator
System administration of Linux and Windows server estates, service desk coordination.
Kautex Textron, Avnet, D-Logistics (Bosch), TNT Contract Logistics / Black & Decker, AKS Benelux
Logistics Manager
Logistics management, including a department of 55 people. Ran ISO, Lean and Six Sigma projects.
A.06 — Certifications & trainings
Judicial Expert in ICT and Security, Ghent University
Full list of certificates of completion on LinkedIn →A.07 — Contact